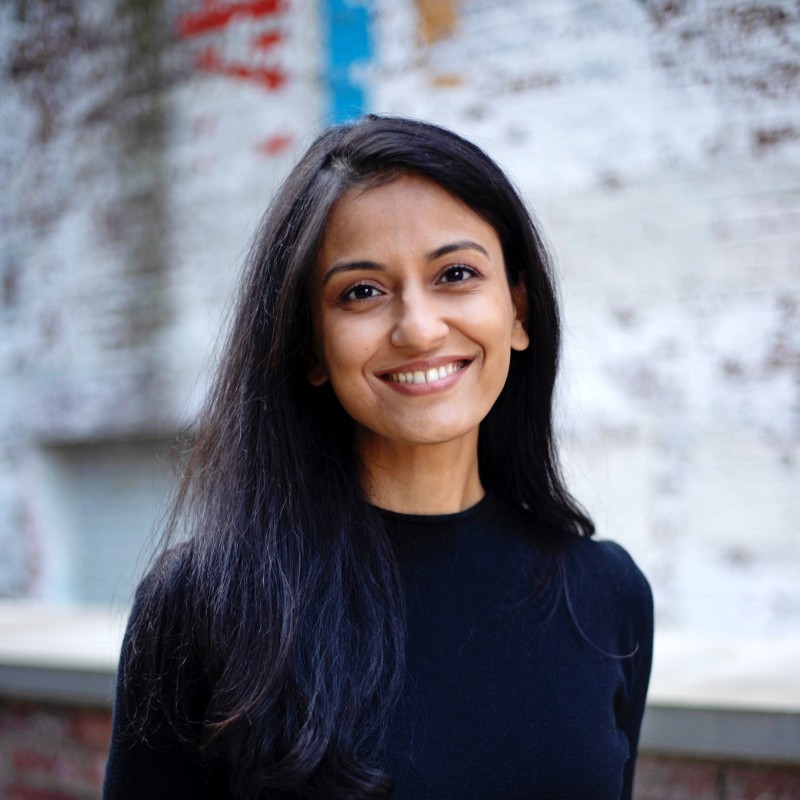
Amita Goyal
CEO
20 years across enterprise sales, corporate finance and legal compliance; ex-WeWork and BCG; works with Fortune 500 clients on go-to-market and governance.
 Meridian
 · AI-Native compliance consulting
We build the management system, implement the controls, get you audit-ready, and operate it.
Powered by custom AI-native software and a dedicated compliance expert.
Why now
Security is no longer enough. Customers increasingly want to understand how AI is used, governed, monitored and escalated.
What models and providers are in use?
What data reaches the model — and where does it go?
What are the risks, guardrails and escalation paths?
Who approves, monitors and documents AI use?
The business risk
If your team cannot answer these questions clearly, AI governance becomes a procurement blocker — not just a compliance project.
Who this is for
If compliance currently lands on the person least able to spare the time, Meridian becomes that function — accountable, embedded and fixed-cost.
You're selling into enterprises and every deal now arrives with a security questionnaire and an ISO 42001 question.
One security lead covering audits, vendor reviews and evidence, with no analyst team to delegate to.
You need a certificate on a deal timeline and no idea which auditor, scope or standard to choose.
Certified once, now drowning in surveillance audits, control drift and recurring customer requests.
The Meridian model
We combine hands-on compliance expertise with software built around your business, so you get the function without building the dept.
Create the AIMS
AI inventory · risk register · policies · controls · technical remediation
Get audit-ready
Evidence · internal review · auditor coordination · audit representation
Keep it alive
Monitoring · access/vendor reviews · annual audits · buyer questionnaires
Result
Enterprise-grade AI governance without incremental compliance headcount or a standalone compliance software stack.
One governance layer
The same policies, controls & evidence can support multiple frameworks, reducing duplicate work as customer requirements expand.
Map once. Prove once. Reuse everywhere.
Hands-on toolkit
Meridian arrives with working knowledge of the platforms auditors expect to see. We implement, configure and evidence controls across your existing stack for both ISO 27001 (ISMS) and ISO 42001 (AIMS) — no re-platforming, no shelf-ware.
ISMS · ISO 27001
From the ISMS document registry to penetration tests and device management, we wire these tools into a single, evidence-backed management system.
GRC & ISMS platforms
Vanta — ISMS automation & document registry
Secureframe — ISMS document registry
+2 more
Devices & identity
Kandji — Mobile device management
JumpCloud — Directory & device trust
+2 more
Testing & vulnerability management
Wallarm — API & vulnerability management
Cobalt — Penetration testing
+2 more
Logging, SIEM & tracking
Elastic — SIEM & log management
Datadog — Observability & error handling
+2 more
Control areas we implement & maintain
AIMS · ISO 42001
AI gateways, policy-as-code authorization, cost control, rate limiting, full LLM logging and a cryptographically verifiable evidence registry — the technical backbone of a living AIMS.
AI gateways & model routing
LiteLLM — Unified AI gateway & model routing
Portkey — AI gateway with guardrails
+2 more
Policy, authorization & guardrails
Open Policy Agent — Policy-as-code authorization
Cloudflare AI Gateway — Gateway policies & rate limiting
+2 more
Cost control, rate limits & logs
Helicone — LLM cost control & rate limiting
Langfuse — LLM traces, logs & evaluation
+2 more
Evidence & registries
AIR evidence registry — Cryptographically verifiable evidence
Vanta — Control evidence collection
+2 more
Control areas we implement & maintain
Already standardized on different vendors? We implement controls in your stack — these are examples of platforms we've run in production audits.
"The Meridian team have supported us as our virtual compliance team for over five years. They handled the full cycle of our ISO 27001 certification and our AI compliance work, and they help our sales team with day-to-day PSA requests from every corporate client we deal with."

The economics
The alternative is not just a software license — it is the people, consultants and internal time required to make the program actually work.
One accountable fee. No separate compliance team to build and no standalone software stack to administer.
Who you actually work with
Our leadership brings decades of combined experience across startups, Fortune 500 clients and compliance, including full-cycle ISO 27001 and ISO 42001 certifications and enterprise PSA processes for corporate clients such as bettercoach.io.
CEO
20 years across enterprise sales, corporate finance and legal compliance; ex-WeWork and BCG; works with Fortune 500 clients on go-to-market and governance.
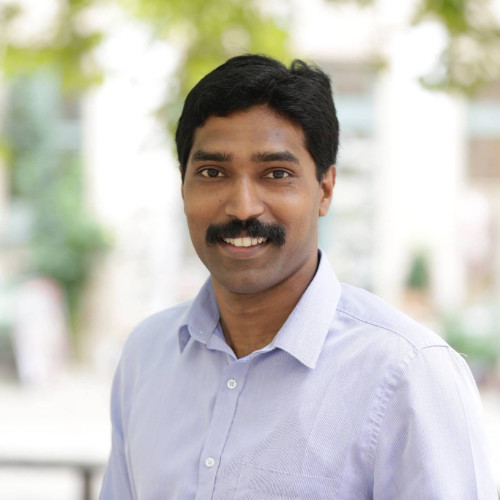
CTO
18 years as CTO and CISO for two unicorns (Grover, Circles.Life) and enterprises including BCG, Cisco and ASML; delivered ISO implementations for 10+ corporate clients.
Founding Engineer
Ex-Meta engineer shipping full-stack products; built internal tools at Meta and Fintech features at Heron Finance and Común.
Start your certification
We'll run a no-obligation gap analysis and map the fastest route to certification. A senior consultant replies within one business day.